Critical UEFI Firmware Flaw Threatens Global Server Infrastructure
· GlobeWire Daily Science Desk · Source: arstechnica.com
Image: arstechnica.com — Creative Commons
Understanding the Vulnerability
A high-severity vulnerability, tracked as CVE-2026-97631, has been identified in the TianoCore EDK II firmware codebase. With a severity rating of 9.5, the flaw resides in the PXE-Base Code driver, which handles network-based booting. An attacker with local network access can trigger a buffer overflow by sending oversized ICMP error messages, potentially executing malicious code at the CPU's most privileged level (Ring 0) during the boot process.
Impact and Mitigation
This flaw primarily affects enterprise servers and data centers utilizing network booting. Unlike consumer hardware booting from local disks, these systems are uniquely exposed. While no evidence suggests it serves as an initial entry point for network infiltration, it could facilitate privilege escalation. Administrators should contact hardware vendors for firmware updates and consider disabling network boot configurations as a temporary precaution. Details can be found at https://arstechnica.com/security/2026/10/code-execution-flaw-in-uefi-firmware-threatens-most-servers-on-planet-earth/.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 NASA's NEO Surveyor Mission Reaches Key Milestone With Sunshade and Solar Array Integration
 Global Anti-Data Center Movement Offers Lessons for US Communities Facing AI Infrastructure Boom
 Boston Dynamics Employees Push Back Against ICE Robot Dog Contract
 Telehealth Platform Hims Expands Into Testosterone Replacement Therapy
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
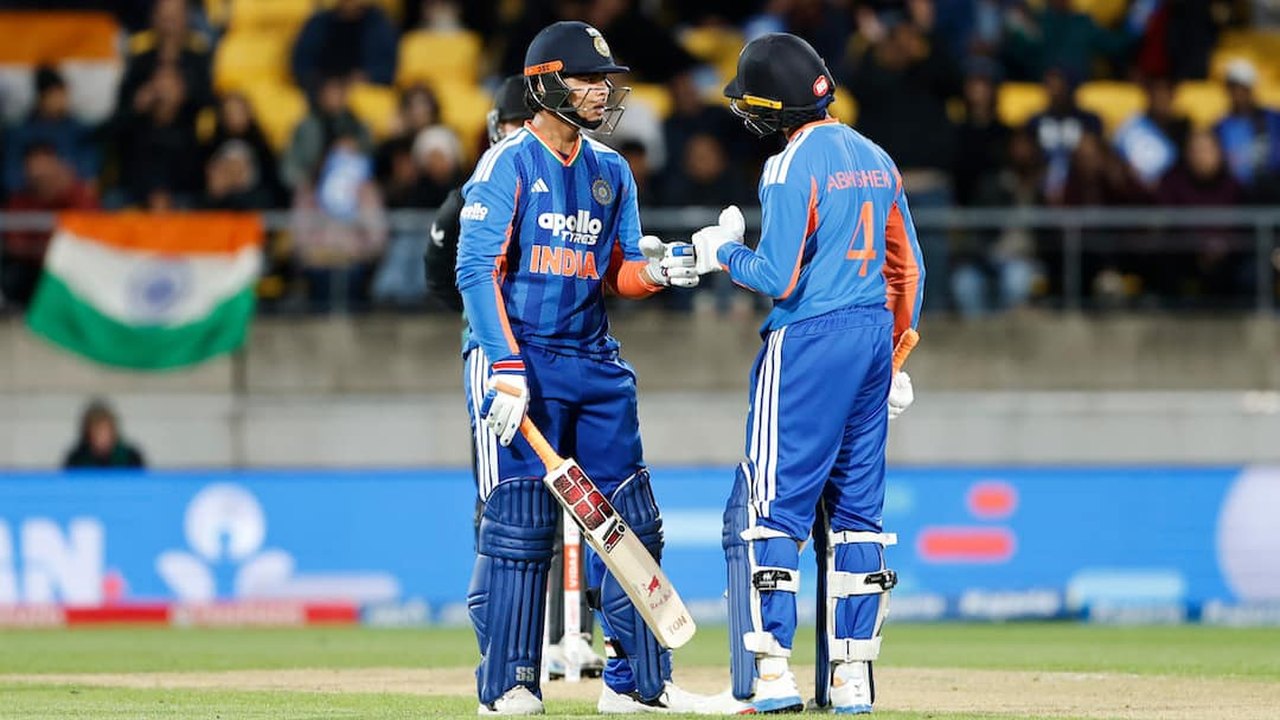 India Sets New Men's T20I Powerplay World Record Against New ZealandGlobal Anti-Data Center Movement Offers Lessons for US Communities Facing AI Infrastructure Boom
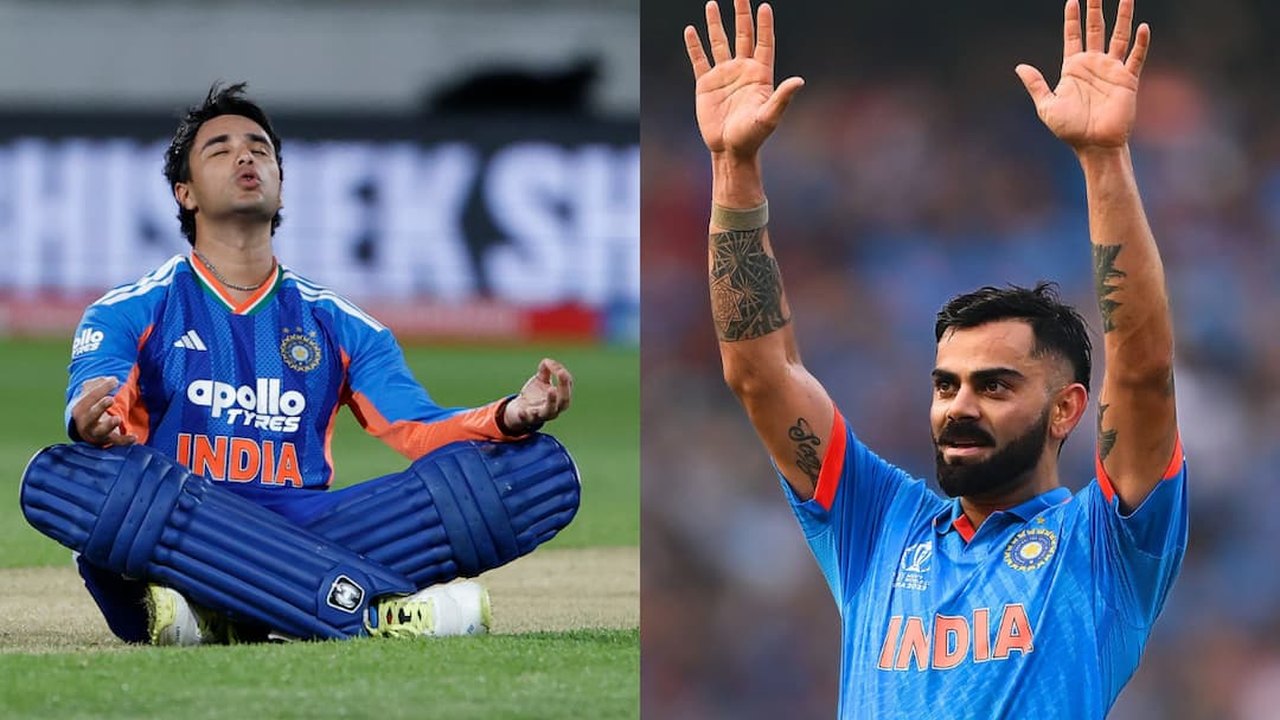 Abhishek Sharma Surpasses Kohli, Makes T20 History With 35-Ball Century Against New Zealand
 Campaigners Warn Government Over Cumulative Climate Impact of Pending Policy Decisions
 India’s Oscar Entry ‘Gondhal’ Debuts Global Trailer as Awards Campaign Intensifies
 Bharat Biotech and VeGen Bio Partner to Advance CAR-T Cell Therapy for Multiple Myeloma with 2028 Indian Launch Target